New details about FBI probe that led to Chinese spy’s conviction
May 19, 2014 Leave a comment
 By JOSEPH FITSANAKIS | intelNews.org
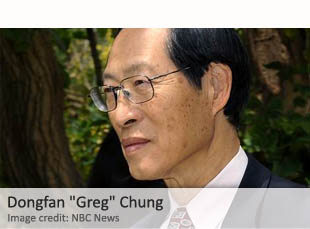
Some of our longtime readers will recall the case of Dongfan “Greg” Chung, a Chinese-born American engineer for Boeing, who was convicted in 2009 of passing US space program secrets to China. The case is arguably far more important than it might have seemed at the time, as Chung was technically the first American to be jailed for economic espionage. Many at the Federal Bureau of Investigation view the Chung conviction as a landmark case for providing clear legal proof of Chinese espionage in the US. Little is known, however, about how the FBI managed to uncover Chung’s espionage activities, which are believed to have gone on for nearly three decades. In the latest issue of The New Yorker, Yudhijit Bhattachargjee reveals for the first time the fascinating background of how the Bureau got to Chung. It did so through another American engineer of Chinese origin, named Chi Mak. Unlike Chung, who was ideologically committed to Maoism and was recruited by Chinese intelligence after immigrating to the US, Mak was an accredited intelligence operative who was allegedly specifically planted in the US by the Chinese. He came to America from Hong Kong in 1979 and worked for California-based defense contractor Power Paragon. He almost immediately began stealing secrets relating to US Navy systems. The FBI first started monitoring Mak and his wife, Rebecca, in 2004, following a tip. The effort evolved in one of the Bureau’s biggest counterintelligence cases, involving elaborate physical and electronic surveillance that lasted for nearly 18 months. During that time, FBI and Naval Criminal Investigation Service agents installed surveillance cameras outside the Maks’ residence, followed the suspects around, and monitored their telephone calls. Eventually, the surveillance team managed to acquire a warrant allowing them to clandestinely enter the Maks’ home and conduct a secret search. The nondestructive entry team discovered numerous stacks of secret documents “some two or three feet high” all around the suspects’ house. Among the findings was an address book containing the names of other engineers of Chinese origin living in the state of California. That, says Bhattachargjee, was the first time the FBI came across Chung’s name. Read more of this post






The mysterious Chinese unit behind the cyberespionage charges
May 20, 2014 by Joseph Fitsanakis 2 Comments
On Monday, the United States government leveled for the first time charges against a group of identified Chinese military officers, allegedly for stealing American trade secrets through cyberespionage. The individuals named in the indictment are all members of a mysterious unit within the Chinese People’s Liberation Army (PLA) command structure, known as Unit 61398. It is estimated that the unit has targeted at least 1,000 private or public companies and organizations in the past 12 years. Western cybersecurity experts often refer to the group as “APT1”, which stands for “Advanced Persistent Threat 1”, or “Byzantine Candor”. It is believed to operate under the Second Bureau of the PLA’s General Staff Department, which is responsible for collecting foreign military intelligence. Many China military observers argue that Unit 61398 is staffed by several thousand operatives, who can be broadly categorized into two groups: one consisting of computer programmers and network operations experts, and the other consisting of English-language specialists, with the most talented members of the Unit combining both skills. Computer forensics experts have traced the Unit’s online activities to several large computer networks operating out of Shanghai’s Pudong New Area district, a heavily built neighborhood in China’s largest city, which serves as a symbol of the country’s rapid industrialization and urbanization. Among other things, Unit 61398 is generally accused of being behind Operation SHADY RAT, one of history’s most extensive known cyberespionage campaigns, which targeted nearly 100 companies, governments and international organizations, between 2006 and 2011. The operation is believed to be just one of numerous schemes devised by Unit 61398 in its effort to acquire trade secrets from nearly every country in the world during the past decade, say its detractors. American sources claim that the PLA Unit spends most of its time attacking private, rather than government-run, networks and servers. As the US Attorney General, Eric Holder, told reporters on Monday, Unit 61398 conducts hacking “for no reason other than to advantage state-owned companies and other interests in China, at the expense of businesses here in the United States”. But The Washington Post points out that the recent revelations by US intelligence defector Edward Snowden arguably make it “easier for China to dismiss” Washington’s charges, since they point to Read more of this post
Filed under Expert news and commentary on intelligence, espionage, spies and spying Tagged with Advanced Persistent Threat 1, Analysis, Byzantine Candor, China, Chinese People's Liberation Army, computer hacking, cyberespionage, economic espionage, News, operation SHADY RAT, Unit 61398