Comment: Who authored computer virus that ‘dwarfs Stuxnet’?
June 6, 2012 9 Comments
 By JOSEPH FITSANAKIS | intelNews.org |
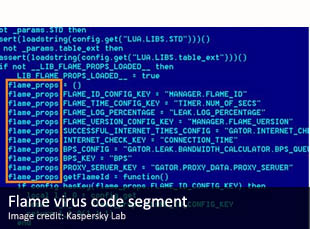
When the Stuxnet computer virus was detected, in 2010, it was recognized as the most sophisticated malware ever created. It had been specifically designed to sabotage Siemens industrial software systems, which were used in Iran’s nuclear energy program. Not surprisingly, most Stuxnet-infected computers were in Iran. Now a new, massive and extremely sophisticated piece of malware has been detected in computers belonging to the Iranian National Oil Company and Iran’s Ministry of Petroleum. It is called Flame and, according to antivirus company Kaspersky Lab, which first spotted the virus last week, it is “one of the most complex threats ever discovered”. Simply consider that Stuxnet, which caused unprecedented waves of panic among Iranian cybersecurity experts, was 500 kilobytes in size. Flame is over 20 megabytes in size, consisting of 650,000 lines of code; it is so complex that it is expected to take programming analysts around a decade to fully comprehend. The two are different, of course. Stuxnet was an infrastructure-sabotaging malware, which destroyed hundreds —maybe even thousands—of Iranian nuclear centrifuges. Flame, on the other hand, appears to be an espionage tool: it aims to surreptitiously collect information from infected systems. What connects them is their intended target: Iran. We now have Stuxnet, the most complex sabotaging malware ever discovered, which must have taken dozens of programmers several months to create, and Flame, the world’s most powerful cyberespionage tool ever detected by computer security experts. And both have been primarily directed at Iranian government computers. Read more of this post







Russian colonel was ‘most successful CIA spy’ in recent years
June 7, 2012 by Joseph Fitsanakis 1 Comment
Before the dust could settle from last month’s closed-door trial of Vladimir Lazar, and the arrest of an unnamed missile engineer on charges of espionage, Russia claims to have exposed yet another spy. Valery Mikhailov, a retired Russian counterintelligence officer, has been given an 18-year prison sentence for allegedly spying on behalf of the United States Central Intelligence Agency. In disclosing Mikhailov’s sentence yesterday, Moscow District Military Court officials were deliberately vague about Mikhailov’s alleged espionage activities, and provided limited information on the precise charges against him. But reporters, who were not allowed to attend Mikhailov’s trial, were told that he voluntarily approached CIA officers in Russia in 2001 and offered to spy on his country on behalf of the US, in exchange for regular payments in cash. Russian government prosecutors said that, from 2001 until 2007, when his activities were detected by Russia’s Federal Security Service (FSB), Mikhailov gave his American handlers access to over a thousand copies of secret or top-secret documents. Most of these, according to reports in the Russian media, had been prepared by FSB analysts for top-level Russian government officials, including the President, Prime Minister, and members of the Security Council of the Russian Federation. Russian government prosecutors say that Mikhailov was arrested following an extensive period of surveillance by the FSB, which allegedly resulted in the capture of an American CIA courier. The latter was apprehended while surreptitiously collecting classified documents copied by Mikhailov. Following his arrest, Mikhailov is said to have admitted that he earned over $2 million from his espionage activities. Read more of this post
Filed under Expert news and commentary on intelligence, espionage, spies and spying Tagged with CIA, counterintelligence, espionage, FSB, imprisoned spy swaps, News, Russia, United States, Valery Mikhailov, Viktor Bout